link1s.site

Exclusive: India's Paytm gets government panel nod to invest in payments arm, sources say

NEW DELHI, July 9 (Reuters) - India's beleaguered Paytm (PAYT.NS), opens new tab has secured approval from a government panel that oversees investments linked to China to invest 500 million rupees ($6 million) in a key subsidiary, three sources with direct knowledge of the matter said.

The approval, which still has to be vetted by the finance ministry, will remove the main stumbling block to the unit, Paytm Payment Services, resuming normal business operations.

Paytm Payment Services is one of the biggest remaining parts of the fintech firm's business, accounting for a quarter of consolidated revenue in the financial year ended March 2023.

A separate unit, Paytm Payments Bank, was wound down this year by order of the central bank due to persistent compliance issues, triggering a meltdown in Paytm's stock.

The government panel had earlier held back approval due to concerns about the 9.88% stake in Paytm held by China's Ant Group. India has intensified scrutiny of Chinese businesses since a 2020 border clash between the two countries.

All in all, Paytm has been waiting for the nod from the government panel for about two years and without it, it would have had to also wind down its payment services business, which was forbidden from taking on new customers in March 2023.

Once the approval has been formalised, it will be able to seek a so-called "payment aggregator" licence from the Reserve Bank of India.

The sources, two of whom are government sources, declined to be identified as the decision has not been formally announced.

India's foreign, home, finance and industries ministries, whose representatives sit on the panel, did not reply to emails seeking comment.

A Paytm spokesperson said the company does not comment on market speculation. "We will continue to make disclosures in compliance with our obligations under the SEBI Regulations, and will inform the exchanges when there is any new material information to share," the spokesperson said.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.
Google extends Linux kernel support to 4 years
According to AndroidAuthority, the Linux kernel used by Android devices is mostly derived from Google's Android Universal Kernel (ACK) branch, which is created from the Android mainline kernel branch when new LTS versions are released upstream. For example, when kernel version 6.6 is announced as the latest LTS release, an ACK branch for Android15-6.6 appears shortly after, with the "android15" in the name referring to the Android version of the kernel (in this case, Android 15). Google maintains its own set of LTS kernel branches for three main reasons. First, Google can integrate upstream features that have not yet been released into the ACK branch by backporting or picking, so as to meet the specific needs of Android. Second, Google can include some features that are being developed upstream in the ACK branch ahead of time, making it available for Android devices as early as possible. Finally, Google can add some vendor or original equipment manufacturer (OEM) features for other Android partners to use. Once created, Google continues to update the ACK branch to include not only bug fixes for Android specific code, but also to integrate the LTS merge content of the upstream kernel branch. For example, the Linux kernel vulnerability disclosed in the July 2024 Android security bulletin will be fixed through these updates. However, it is not easy to distinguish a bug fix from other bug fixes, as a patch that fixes a bug may also accidentally plug a security vulnerability that the submitter did not know about or chose not to disclose. Google does its best to recognize this, but it inevitably misses the mark, resulting in bug fixes for the upstream Linux kernel being released months before Android devices. As a result, Google has been urging Android vendors to regularly update the LTS kernel to avoid being caught off guard by unexpectedly disclosed security vulnerabilities. Clearly, the LTS version of the Linux kernel is critical to the security of Android devices, helping Google and vendors deal with known and unknown security vulnerabilities. The longer the support period, the more timely security updates Google and vendors can provide to devices.
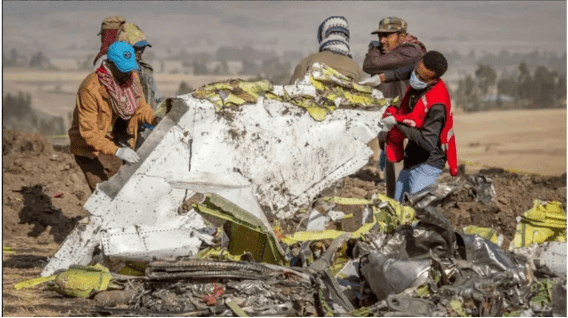
Boeing will be fined 3.5 billion yuan for "conspiracy to defraud" in two air crashes. Will the company slide into the abyss?
Taking the initiative to plead guilty to Boeing is not small, but it can avoid being exposed to more problems when it is publicly tried, which is a "minor penalty" for Boeing. So now the families of the crash victims are very opposed to the move, demanding that the trial continue to be open. But after all, Boeing is America's oldest industrial son, whether it is Trump or Biden, and finally have to gently put down, give a chance. The Justice Department had been seeking a guilty plea from Boeing as early as May, when it launched the investigation. After all, if you plead guilty, you only need to pay a fine, and if you really go to court, you don't know how many quality problems Boeing will be exposed by your witnesses. Boeing also knew it had too many flaws, and paying a $243.6 million fine and bringing in a third party to monitor its compliance for three years, totaling more than $400 million in additional expenses, is small change for Boeing. Given Boeing's style in the past few years, this fine may not even force Boeing to tighten production line management. Just this kind of "reconciliation" that completely excludes the victims of the crash can not get the families to agree. Paul Cassell, an attorney for the victims' families, said he plans to ask the federal judge overseeing the case to reject the agreement and "hold this case to an open trial so that all the facts of this case can be presented in a fair and public manner before a jury." The demand is reasonable, but the US judge will most likely side with Boeing.
Exclusive: India's Paytm gets government panel nod to invest in payments arm, sources say
NEW DELHI, July 9 (Reuters) - India's beleaguered Paytm (PAYT.NS), opens new tab has secured approval from a government panel that oversees investments linked to China to invest 500 million rupees ($6 million) in a key subsidiary, three sources with direct knowledge of the matter said. The approval, which still has to be vetted by the finance ministry, will remove the main stumbling block to the unit, Paytm Payment Services, resuming normal business operations. Paytm Payment Services is one of the biggest remaining parts of the fintech firm's business, accounting for a quarter of consolidated revenue in the financial year ended March 2023. A separate unit, Paytm Payments Bank, was wound down this year by order of the central bank due to persistent compliance issues, triggering a meltdown in Paytm's stock. The government panel had earlier held back approval due to concerns about the 9.88% stake in Paytm held by China's Ant Group. India has intensified scrutiny of Chinese businesses since a 2020 border clash between the two countries. All in all, Paytm has been waiting for the nod from the government panel for about two years and without it, it would have had to also wind down its payment services business, which was forbidden from taking on new customers in March 2023. Once the approval has been formalised, it will be able to seek a so-called "payment aggregator" licence from the Reserve Bank of India. The sources, two of whom are government sources, declined to be identified as the decision has not been formally announced. India's foreign, home, finance and industries ministries, whose representatives sit on the panel, did not reply to emails seeking comment. A Paytm spokesperson said the company does not comment on market speculation. "We will continue to make disclosures in compliance with our obligations under the SEBI Regulations, and will inform the exchanges when there is any new material information to share," the spokesperson said.
OpenAI's internal AI details stolen in 2023 breach, NYT reports
July 4 (Reuters) - A hacker gained access to the internal messaging systems at OpenAI last year and stole details about the design of the company's artificial intelligence technologies, the New York Times reported, opens new tab on Thursday. The hacker lifted details from discussions in an online forum where employees talked about OpenAI's latest technologies, the report said, citing two people familiar with the incident. However, they did not get into the systems where OpenAI, the firm behind chatbot sensation ChatGPT, houses and builds its AI, the report added. OpenAI executives informed both employees at an all-hands meeting in April last year and the company's board about the breach, according to the report, but executives decided not to share the news publicly as no information about customers or partners had been stolen. OpenAI executives did not consider the incident a national security threat, believing the hacker was a private individual with no known ties to a foreign government, the report said. The San Francisco-based company did not inform the federal law enforcement agencies about the breach, it added. OpenAI in May said it had disrupted five covert influence operations that sought to use its AI models for "deceptive activity" across the internet, the latest to stir safety concerns about the potential misuse of the technology. The Biden administration was poised to open up a new front in its effort to safeguard the U.S. AI technology from China and Russia with preliminary plans to place guardrails around the most advanced AI Models including ChatGPT, Reuters earlier reported, citing sources.