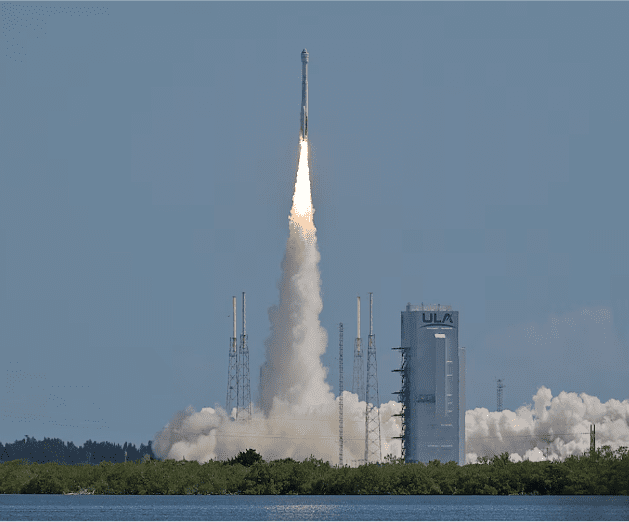
Explainer: How Boeing's Starliner can bring its astronauts back to Earth
WASHINGTON, June 24 (Reuters) - Problems with Boeing's Starliner capsule, still docked at the International Space Station (ISS), have upended the original plans for its return of its two astronauts to Earth, as last-minute fixes and tests draw out a mission crucial to the future of Boeing's (BA.N), opens new tab space division. NASA has rescheduled the planned return three times, and now has no date set for it. Since its June 5 liftoff, the capsule has had five helium leaks, five maneuvering thrusters go dead and a propellant valve fail to close completely, prompting the crew in space and mission managers in Houston to spend more time than expected pursuing fixes mid-mission. Here is an explanation of potential paths forward for Starliner and its veteran NASA astronauts, Barry "Butch" Wilmore and Sunita "Suni" Williams. THE CURRENT SITUATION Starliner can stay docked at the ISS for up to 45 days, according to comments by NASA's commercial crew manager Steve Stich to reporters. But if absolutely necessary, such as if more problems arise that mission officials cannot fix in time, it could stay docked for up to 72 days, relying on various backup systems, according to a person familiar with flight planning. Internally at NASA, Starliner's latest targeted return date is July 6, according to this source, who spoke on condition of anonymity. Such a return date would mean that the mission, originally planned for eight days, instead would last a month. Starliner's expendable propulsion system is part of the craft's "service module." The current problems center on this system, which is needed to back the capsule away from the ISS and position it to dive through Earth's atmosphere. Many of Starliner's thrusters have overheated when fired, and the leaks of helium - used to pressurize the thrusters - appear to be connected to how frequently they are used, according to Stich.
Stanford AI project team apologizes for plagiarizing Chinese model
An artificial intelligence (AI) team at Stanford University apologized for plagiarizing a large language model (LLM) from a Chinese AI company, which became a trending topic on the Chinese social media platforms, where it sparked concern among netizens on Tuesday. We apologize to the authors of MiniCPM [the AI model developed by a Chinese company] for any inconvenience that we caused for not doing the full diligence to verify and peer review the novelty of this work, the multimodal AI model Llama3-V's developers wrote in a post on social platform X. The apology came after the team from Stanford University announced Llama3-V on May 29, claiming it had comparable performance to GPT4-V and other models with the capability to train for less than $500. According to media reports, the announcement published by one of the team members quickly received more than 300,000 views. However, some netizens from X found and listed evidence of how the Llama3-V project code was reformatted and similar to MiniCPM-Llama3-V 2.5, an LLM developed by a Chinese technology company, ModelBest, and Tsinghua University. Two team members, Aksh Garg and Siddharth Sharma, reposted a netizen's query and apologized on Monday, while claiming that their role was to promote the model on Medium and X (formerly Twitter), and that they had been unable to contact the member who wrote the code for the project. They looked at recent papers to validate the novelty of the work but had not been informed of or were aware of any of the work by Open Lab for Big Model Base, which was founded by the Natural Language Processing Lab at Tsinghua University and ModelBest, according to their responses. They noted that they have taken all references to Llama3-V down in respect to the original work. In response, Liu Zhiyuan, chief scientist at ModelBest, spoke out on the Chinese social media platform Zhihu, saying that the Llama3-V team failed to comply with open-source protocols for respecting and honoring the achievements of previous researchers, thus seriously undermining the cornerstone of open-source sharing. According to a screenshot leaked online, Li Dahai, CEO of ModelBest, also made a post on his WeChat moment, saying that the two models were verified to have highly similarity in terms of providing answers and even the same errors, and that some relevant data had not yet been released to the public. He said the team hopes that their work will receive more attention and recognition, but not in this way. He also called for an open, cooperative and trusting community environment. Director of the Stanford Artificial Intelligence Laboratory Christopher Manning also responded to Garg's explanation on Sunday, commenting "How not to own your mistakes!" on X. As the incident became a trending topic on Sina Weibo, Chinese netizens commented that academic research should be factual, but the incident also proves that the technology development in China is progressing. Global Times
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.
Will chatGPT lead to job losses?
In fact, ChatGPT can bring more opportunities to many industries, such as customer service, marketing, speech recognition, and more. ChatGPT can help businesses engage with customers more effectively, improve the customer experience, and give businesses more time and resources to focus on other tasks. Come to see While ChatGPT can replace humans in certain situations, it is not a complete replacement for humans. In many cases, human-to-human communication is still the most effective way. Therefore, the emergence of ChatGPT will not lead to the unemployment of all people, but will cause structural changes in the labor force and the redistribution of occupations.