link1s.site

World's deepest diving pool opens in Poland, 45.5 meters deep

The world's deepest diving pool, Deepspot, opened this weekend near the Polish capital Warsaw. The 45.5-meter pool contains artificial underwater caves, Mayan ruins and a small shipwreck for scuba divers and free divers to explore.

Deepspot can hold 8,000 cubic meters of water, more than 20 times the capacity of a normal 25-meter swimming pool.

Unlike ordinary swimming pools, Deepspot can still open despite Poland's COVID-19 epidemic prevention restrictions because it is a training center that provides courses.

The operator also plans to open a hotel where guests can observe divers at a depth of 5 meters from their rooms.

"This is the deepest diving pool in the world," Michael Braszczynski, 47, Deepspot's director and a diving enthusiast, told AFP at the opening yesterday.

The current Guinness World Record holder is a 42-meter-deep pool in Montegrotto Terme, Italy. The 50-meter-deep Blue Abyss pool in the UK is scheduled to open in 2021.

On the first day of Deepspot's opening, about a dozen people visited, including eight experienced divers who wanted to pass the instructor exam.

"There are no spectacular fish or coral reefs here, so it can't replace the ocean, but it is certainly a good place to learn and train safe open water diving," said 39-year-old diving instructor Przemyslaw Kacprzak.

"And it's fun! It's like a kindergarten for divers."
See Pregnant Margot Robbie Debut Her Baby Bump
This Barbie is going to be a mother. And Margot Robbie has no problem putting her burgeoning baby bump on full display. In fact, the Barbie star, who is pregnant with her Tom Ackerley’s first baby, debuted recently her bump while vacationing on Italy’s Lake Como with her husband July 7. For the outing, Margot donned a black blazer over a white tee that was cropped above her stomach, showing off a sweet baby bump. She finished off the look with low-rise black trousers, black platform sandals and a summery straw bag. For his part, Tom—whom Margot wed in a 2016 ceremony in her native Australia—wore olive green trousers and a cream-colored button-down shirt and tan sneakers. The couple were photographed waiting on a dock in Lake Como before they hopped in a boat and sailed off into a literal sunset. While Margot and Tom, both 34, haven’t spoken publicly about their upcoming bundle of joy, the I, Tonya alum has previously expressed hope to have a big family one day. As she told Porter in 2018, “If I'm looking into my future 30 years from now, I want to see a big Christmas dinner with tons of kids there.” Tom and Margot’s new chapter comes over ten years after their love story first began on the set of 2014's Suite Française, in which Margot starred while Tom worked as a third assistant director. But while she was immediately smitten, Margot was convinced her love would go unrequited. "I was always in love with him, but I thought, ‘Oh, he would never love me back,'" she admitted to Vogue in 2016. "'Don't make it weird, Margot. Don't be stupid and tell him that you like him.' And then it happened, and I was like, ‘Of course we're together. This makes so much sense, the way nothing has ever made sense before.'"
Ukrainian Presidential Office: Russia's attacks on multiple locations in Ukraine have killed 36 people
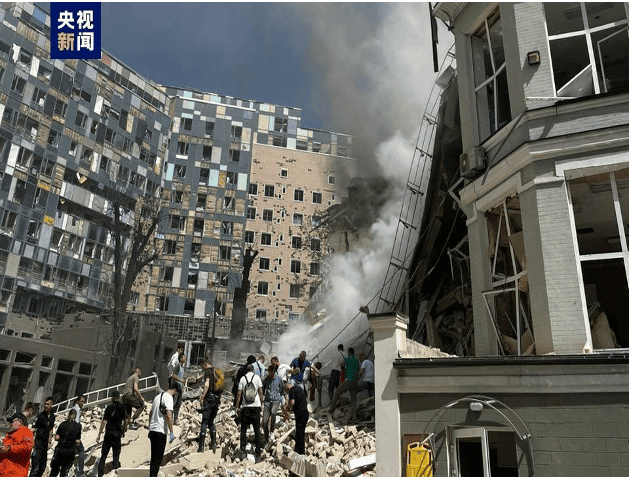
The Ukrainian presidential office said on July 8 local time that Russia's large-scale attacks on many parts of Ukraine have killed 36 people and injured 140 others. According to the Ukrainian State Emergency Service, a total of 619 rescue workers and 132 equipment participated in the rescue work across Ukraine that day. Ukrainian President Zelensky said on social media on the 8th that Russia launched more than 40 missiles of various types at Ukraine that day. Residential buildings and infrastructure in many cities in Ukraine were damaged in varying degrees of attacks, and a children's hospital was destroyed. Rescue departments are currently conducting emergency rescue on the scene. The Russian Ministry of Defense issued a statement on the 8th local time saying that Ukrainian officials' claim that Russia used missiles to attack Ukrainian civilian facilities was untrue. The damage suffered by Kiev was caused by the fall of missiles launched by the city's air defense system.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.
"Corrupt Politicians GPT" "Fiscal Bill GPT", Kenyan protesters use AI to "protest"
In the past few weeks of anti-government activities in Kenya, AI tools have been creatively used by protesters to serve protests. According to the US "Flag" News Agency on July 5, protests in Kenya triggered by the 2024 fiscal bill are still continuing. In the past few weeks, Kenyan protesters, mainly young people, have creatively developed a series of AI tools to assist anti-government activities. The Kenyan government expressed concern about the risks associated with the use of AI tools in protests. Kelvin Onkundi, a software engineer in Kenya, developed the "Fiscal Bill GPT", which operates similarly to ChatGPT and can receive questions about the fiscal bill and generate responses. Martin Siele, a reporter from the "Flag" News Agency, analyzed: "The 'Fiscal Bill GPT' can convert professional terms in many legislative fields into easy-to-understand information for protesters, helping Kenyans understand the potential impact of the fiscal bill." Another software engineer, Marion Kavengi, developed the "SHIF GPT" to provide Kenyans with information about the upcoming Social Health Insurance Fund (SHIF). In addition to AI tools designed to help people understand controversial policies, protesters have also developed "Corrupt Politicians GPT" to assist protest demonstrations. After entering the name of a politician on the platform, the platform will generate a list of corruption scandals about the politician in chronological order. Developer BenwithSon wrote on the social platform X on June 28: "'Corrupt Politicians GPT' allows people to search for any scandal related to any politician. I have seen some leaders stand at the forefront of the political arena, but they are corrupt behind the scenes." Kenyan Chief Minister and Foreign Minister Mudavadi issued a communiqué to ambassadors of various countries in Nairobi on July 2 local time on protests and relevant government measures, expressing concerns about the use of AI and false information in protests. Mudavadi said: "AI technology is used by people with ulterior motives, which will fill the global information system with false narratives." The Kenya Times reported on June 30 that AI technology enables people to force the government to increase transparency and strengthen accountability, and its role in Kenyan political activities is becoming increasingly prominent. Martin Siller believes that AI is reshaping African political behavior in many ways. AI is a new tool for both governments and opposition parties in Africa, but Kenya is one of the African countries with the most developers, and its young protesters are particularly good at using AI technology to fight the government. The 2024 fiscal bill voted and passed by the Kenyan National Assembly on June 25 clearly stated that additional taxes will be levied to repay the interest on high sovereign debt, triggering large-scale demonstrations. After President Ruto announced the withdrawal of the tax increase bill on the evening of the 26th, demonstrations in many parts of Kenya continued. According to Reuters on July 3, Kenyan anti-government protesters are re-adjusting their activities to prevent the protests from turning into violent incidents.
Google extends Linux kernel support to 4 years
According to AndroidAuthority, the Linux kernel used by Android devices is mostly derived from Google's Android Universal Kernel (ACK) branch, which is created from the Android mainline kernel branch when new LTS versions are released upstream. For example, when kernel version 6.6 is announced as the latest LTS release, an ACK branch for Android15-6.6 appears shortly after, with the "android15" in the name referring to the Android version of the kernel (in this case, Android 15). Google maintains its own set of LTS kernel branches for three main reasons. First, Google can integrate upstream features that have not yet been released into the ACK branch by backporting or picking, so as to meet the specific needs of Android. Second, Google can include some features that are being developed upstream in the ACK branch ahead of time, making it available for Android devices as early as possible. Finally, Google can add some vendor or original equipment manufacturer (OEM) features for other Android partners to use. Once created, Google continues to update the ACK branch to include not only bug fixes for Android specific code, but also to integrate the LTS merge content of the upstream kernel branch. For example, the Linux kernel vulnerability disclosed in the July 2024 Android security bulletin will be fixed through these updates. However, it is not easy to distinguish a bug fix from other bug fixes, as a patch that fixes a bug may also accidentally plug a security vulnerability that the submitter did not know about or chose not to disclose. Google does its best to recognize this, but it inevitably misses the mark, resulting in bug fixes for the upstream Linux kernel being released months before Android devices. As a result, Google has been urging Android vendors to regularly update the LTS kernel to avoid being caught off guard by unexpectedly disclosed security vulnerabilities. Clearly, the LTS version of the Linux kernel is critical to the security of Android devices, helping Google and vendors deal with known and unknown security vulnerabilities. The longer the support period, the more timely security updates Google and vendors can provide to devices.