link1s.site

Hamas chief says latest Israeli attack on Gaza could jeopardise ceasefire talks

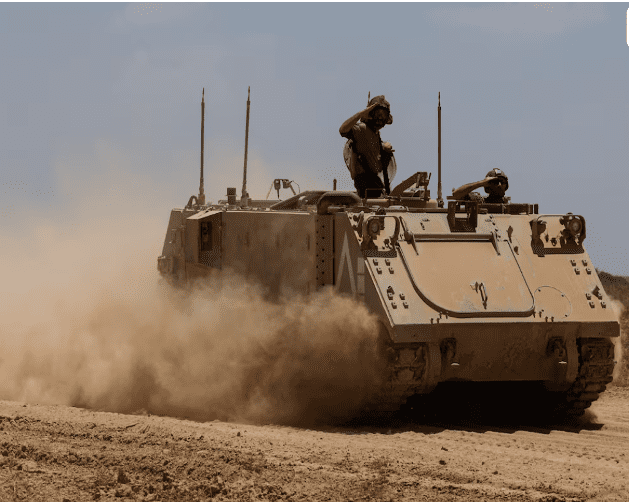
AIRO, July 8 (Reuters) - A new Israeli assault on Gaza on Monday threatened ceasefire talks at a crucial moment, the head of Hamas said, as Israeli tanks pressed into the heart of Gaza City and ordered residents out after a night of massive bombardment.

Residents said the airstrikes and artillery barrages were among the heaviest in nine months of conflict between Israeli forces and Hamas militants in the enclave. Thousands fled.

The assault unfolded as senior U.S. officials were in the region pushing for a ceasefire after Hamas made major concessions last week. The militant group said the new offensive appeared intended to derail the talks and called for mediators to rein in Israel's Prime Minister Benjamin Netanyahu.

The assault "could bring the negotiation process back to square one. Netanyahu and his army will bear full responsibility for the collapse of this path," Hamas quoted leader Ismail Haniyeh as saying.

Gaza City, in the north of the Palestinian enclave, was one of Israel's first targets at the start of the war in October. But clashes with militants there have persisted and civilians have sought shelter elsewhere, adding to waves of displacement. Much of the city lies in ruins.

Residents said Gaza City neighbourhoods were bombed through the night into the early morning hours of Monday. Several multi-storey buildings were destroyed, they said.

The Gaza Civil Emergency Service said it believed dozens of people were killed but emergency teams were unable to reach them because of ongoing offensives.

Gaza residents said tanks advanced from at least three directions on Monday and reached the heart of Gaza City, backed by heavy Israeli fire from the air and ground.

That forced thousands of people out of their homes to look for safer shelter, which for many was impossible to find, and some slept on the roadside.
World's deepest diving pool opens in Poland, 45.5 meters deep
The world's deepest diving pool, Deepspot, opened this weekend near the Polish capital Warsaw. The 45.5-meter pool contains artificial underwater caves, Mayan ruins and a small shipwreck for scuba divers and free divers to explore. Deepspot can hold 8,000 cubic meters of water, more than 20 times the capacity of a normal 25-meter swimming pool. Unlike ordinary swimming pools, Deepspot can still open despite Poland's COVID-19 epidemic prevention restrictions because it is a training center that provides courses. The operator also plans to open a hotel where guests can observe divers at a depth of 5 meters from their rooms. "This is the deepest diving pool in the world," Michael Braszczynski, 47, Deepspot's director and a diving enthusiast, told AFP at the opening yesterday. The current Guinness World Record holder is a 42-meter-deep pool in Montegrotto Terme, Italy. The 50-meter-deep Blue Abyss pool in the UK is scheduled to open in 2021. On the first day of Deepspot's opening, about a dozen people visited, including eight experienced divers who wanted to pass the instructor exam. "There are no spectacular fish or coral reefs here, so it can't replace the ocean, but it is certainly a good place to learn and train safe open water diving," said 39-year-old diving instructor Przemyslaw Kacprzak. "And it's fun! It's like a kindergarten for divers."
Google Pixel 9 series phones will use Qualcomm ultrasonic fingerprint recognition technology
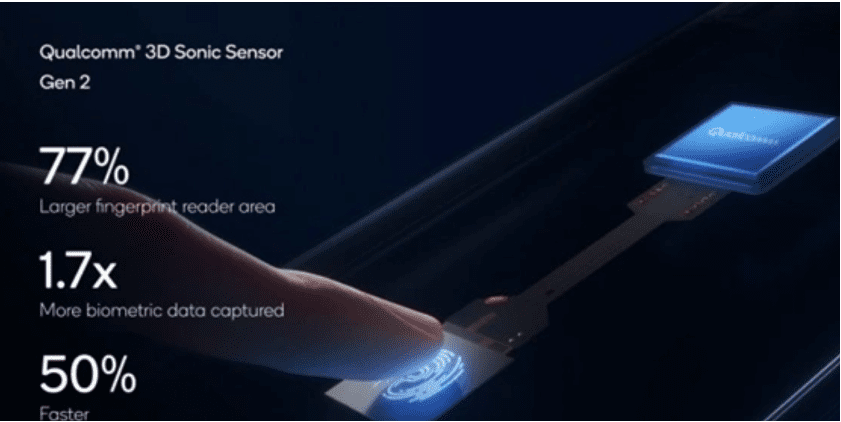
Google's new generation of flagship smartphone Pixel 9 series is expected to be officially released in mid-August, and the new machine is likely to be equipped with ultrasonic fingerprint recognition technology for the first time to replace the original optical fingerprint recognition. According to core intelligence, Google Pixel 9 series will use the same Qualcomm 3D Sonic Gen 2 ultrasonic fingerprint recognition sensor as the Samsung Galaxy S24 Ultra. This ultrasonic technology under the screen fingerprint sensor is Qualcomm released at the CES2021 conference, compared with the previous generation of solutions, the module thickness is further reduced to 0.2mm, while the scanning area is expanded to 8mm×8mm, that is, the recognition area is increased by 77%. This will also allow users to realize fingerprint recognition without having to point their fingertips 100% accurately at the identification area indicated on the screen.
Microsoft to offer Apple devices to employees in China, cites absence of Android services
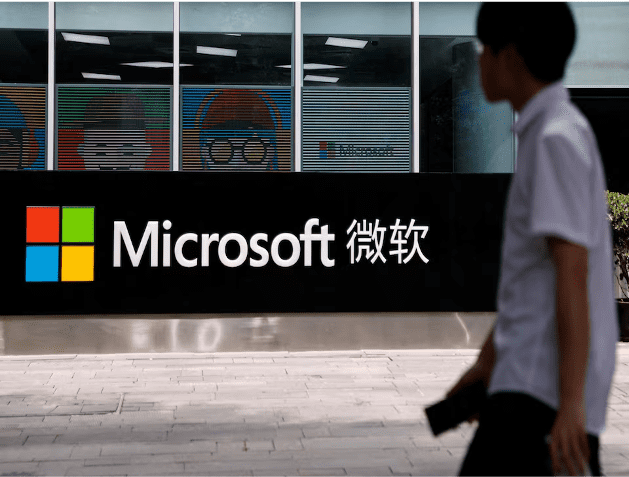
July 8 (Reuters) - Microsoft (MSFT.O), opens new tab intends to offer Apple's (AAPL.O), opens new tab iOS-based devices to its employees in China to access authentication apps, a company spokesperson said on Monday, citing absence of Google's (GOOGL.O), opens new tab Android services in the country. Microsoft has been under increased scrutiny after a series of security breaches, the latest being that of Russian hackers who spied and accessed emails of the company's employees and customers earlier this year. The development was first reported by Bloomberg News, which, citing an internal memo, said the Windows OS-maker instructed its employees in China to use Apple devices at workplace from September. As a part of Microsoft's global Secure Future Initiative, the move to switch to iOS-devices stems from the lack of availability of Google Play Store in China that limits its employees' access to security apps such as Microsoft Authenticator and Identity Pass, the report added. "Due to the lack of availability of Google Mobile Services in this region, we look to offer employees a means of accessing these required apps, such as an iOS device," a company spokesperson told Reuters in an email. Microsoft is among those U.S. companies that have a strong presence in China. It entered the Chinese market in 1992 and also operates a large research and development center in the country. The company will provide iPhone 15 models to employees, currently using Android handsets across China, including Hong Kong, the Bloomberg report said.
MOFCOM refutes EU comments on anti-subsidy investigation into Chinese EVs
A spokesperson for the Ministry of Commerce (MOFCOM) on Monday rejected remarks from the EU Ambassador to China on the anti-subsidy investigation into Chinese electric vehicles (EVs). MOFCOM said China had expressed strong opposition through various channels since October 2023 and has always advocated for handling economic and trade frictions through dialogue and consultation in order to maintain the overall strategic partnership between China and Europe. EU Ambassador to China Jorge Toledo claimed on Sunday that the EU has been trying to engage with China for months regarding the imposition of tariffs on Chinese EVs but that China had only recently sought to initiate discussions. This is false, the spokesperson said. MOFCOM said that after the European Commission (EC) officially filed a case, Chinese Commerce Minister Wang Wentao sent a letter to European Commission Executive Vice-President Valdis Dombrovskis on October 24, 2023, expressing hope to resolve the case through dialogue and negotiation. On November 13, 2023, Wang sent another letter to the European side proposing negotiation suggestions. In February 2024, Wang met with Dombrovskis during the WTO's 13th Ministerial Conference face to face and proposed dialogue and negotiation with the European side. On May 19, 2024, Wang reiterated the hope for dialogue and negotiation to resolve the case in a letter to the European side. Additionally, Chinese technical experts have been sending signals to the European side regarding on-site inspections, hearings, and other channels since the case was filed, expressing willingness to resolve trade frictions through dialogue and negotiation. On the day the preliminary ruling was announced on June 12, Dombrovskis replied to Wang in a letter, expressing the desire for both sides to strengthen dialogue to resolve the case. On June 22, Wang held a video conference with Dombrovskis, and they agreed to start negotiations on the EU's anti-subsidy investigation into Chinese EVs. Subsequently, China sent a working group to Europe for negotiations on June 23, and multiple rounds of technical consultations were held simultaneously via video. MOFCOM said that China has shown the utmost sincerity and hopes that the European side will meet China halfway, show sincerity, and push forward the negotiation process to reach a mutually acceptable solution as soon as possible. China has always believed that trade protectionist measures are not conducive to the development of global green industries and automotive industry cooperation. Efforts should be made to adhere to dialogue and cooperation to promote economic green transformation, rather than creating divisions and disrupting global industrial and supply chains, MOFCOM said. China firmly opposes any unilateralism and protectionism that politicizes and weaponizes economic and trade issues, and will take all necessary measures to defend its own interests against any abuse of rules and suppression of China, MOFCOM added.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.