link1s.site

Stanford AI project team apologizes for plagiarizing Chinese model

An artificial intelligence (AI) team at Stanford University apologized for plagiarizing a large language model (LLM) from a Chinese AI company, which became a trending topic on the Chinese social media platforms, where it sparked concern among netizens on Tuesday.

We apologize to the authors of MiniCPM [the AI model developed by a Chinese company] for any inconvenience that we caused for not doing the full diligence to verify and peer review the novelty of this work, the multimodal AI model Llama3-V's developers wrote in a post on social platform X.

The apology came after the team from Stanford University announced Llama3-V on May 29, claiming it had comparable performance to GPT4-V and other models with the capability to train for less than $500.

According to media reports, the announcement published by one of the team members quickly received more than 300,000 views.

However, some netizens from X found and listed evidence of how the Llama3-V project code was reformatted and similar to MiniCPM-Llama3-V 2.5, an LLM developed by a Chinese technology company, ModelBest, and Tsinghua University.

Two team members, Aksh Garg and Siddharth Sharma, reposted a netizen's query and apologized on Monday, while claiming that their role was to promote the model on Medium and X (formerly Twitter), and that they had been unable to contact the member who wrote the code for the project.

They looked at recent papers to validate the novelty of the work but had not been informed of or were aware of any of the work by Open Lab for Big Model Base, which was founded by the Natural Language Processing Lab at Tsinghua University and ModelBest, according to their responses. They noted that they have taken all references to Llama3-V down in respect to the original work.

In response, Liu Zhiyuan, chief scientist at ModelBest, spoke out on the Chinese social media platform Zhihu, saying that the Llama3-V team failed to comply with open-source protocols for respecting and honoring the achievements of previous researchers, thus seriously undermining the cornerstone of open-source sharing.

According to a screenshot leaked online, Li Dahai, CEO of ModelBest, also made a post on his WeChat moment, saying that the two models were verified to have highly similarity in terms of providing answers and even the same errors, and that some relevant data had not yet been released to the public.

He said the team hopes that their work will receive more attention and recognition, but not in this way. He also called for an open, cooperative and trusting community environment.

Director of the Stanford Artificial Intelligence Laboratory Christopher Manning also responded to Garg's explanation on Sunday, commenting "How not to own your mistakes!" on X.

As the incident became a trending topic on Sina Weibo, Chinese netizens commented that academic research should be factual, but the incident also proves that the technology development in China is progressing.

Global Times
World's deepest diving pool opens in Poland, 45.5 meters deep
The world's deepest diving pool, Deepspot, opened this weekend near the Polish capital Warsaw. The 45.5-meter pool contains artificial underwater caves, Mayan ruins and a small shipwreck for scuba divers and free divers to explore. Deepspot can hold 8,000 cubic meters of water, more than 20 times the capacity of a normal 25-meter swimming pool. Unlike ordinary swimming pools, Deepspot can still open despite Poland's COVID-19 epidemic prevention restrictions because it is a training center that provides courses. The operator also plans to open a hotel where guests can observe divers at a depth of 5 meters from their rooms. "This is the deepest diving pool in the world," Michael Braszczynski, 47, Deepspot's director and a diving enthusiast, told AFP at the opening yesterday. The current Guinness World Record holder is a 42-meter-deep pool in Montegrotto Terme, Italy. The 50-meter-deep Blue Abyss pool in the UK is scheduled to open in 2021. On the first day of Deepspot's opening, about a dozen people visited, including eight experienced divers who wanted to pass the instructor exam. "There are no spectacular fish or coral reefs here, so it can't replace the ocean, but it is certainly a good place to learn and train safe open water diving," said 39-year-old diving instructor Przemyslaw Kacprzak. "And it's fun! It's like a kindergarten for divers."
TSX futures rise ahead of Fed chair Powell's testimony
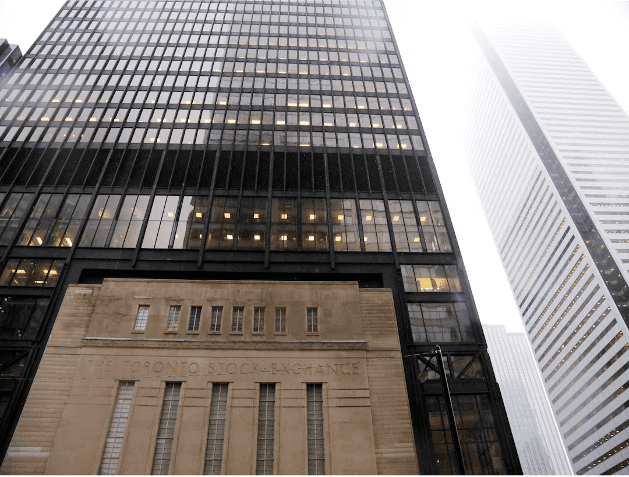
July 9 (Reuters) - Futures linked to Canada's main stock index rose on the back of metal prices on Tuesday, while investors awaited U.S. Federal Reserve Chair Jerome Powell's congressional testimony on monetary policy later in the day. The S&P/TSX 60 futures were up 0.25% by 06:28 a.m. ET (1028 GMT). The Toronto Stock Exchange's materials sector was set to re Oil futures , dipped as fears over supply disruption eased after Hurricane Beryl, which hit major refineries along with the U.S. Gulf Coast, caused minimal impact. Markets will be heavily focussed on Powell's two-day monetary policy testimony before the Senate Banking Committee, starting at 10 a.m. ET (1400 GMT), which can help investors gauge the Fed's rate-cut path. Following last week's softer jobs data, market participants are now pricing in a 77% chance of a rate cut by the U.S. central bank in September. The main macro event for the markets this week will be the U.S. consumer prices data due on Thursday, which can help assess the trajectory of inflation in the world' biggest economy. Wall Street futures were also up on Tuesday after the S&P 500 (.SPX), opens new tab and Nasdaq (.IXIC), opens new tab touched record closing highs in the previous session. In Canada, fears of the economy slipping into recession advanced after the latest data showed that the unemployment rate rose to a 29-month high in June. Traders are now pricing in a 65% chance of another cut by the Bank of Canada, which already trimmed interest rates last month. In corporate news, Cenovus Energy (CVE.TO), opens new tab said it is demobilizing some staff at its Sunrise oil sands project in northern Alberta as a precaution due to the evolving wildfire situation in the area.
Ukrainian Presidential Office: Russia's attacks on multiple locations in Ukraine have killed 36 people
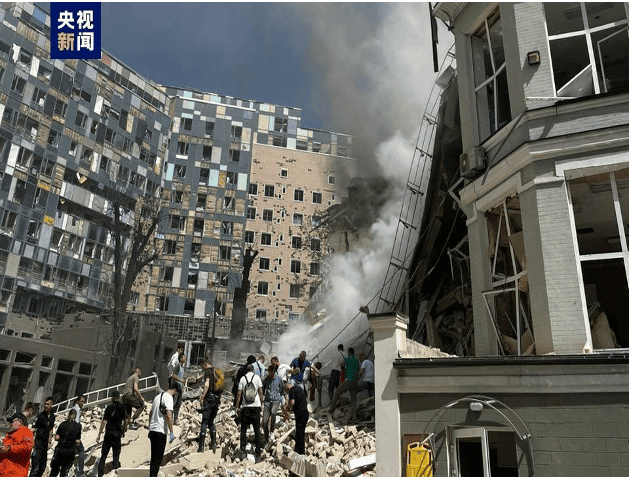
The Ukrainian presidential office said on July 8 local time that Russia's large-scale attacks on many parts of Ukraine have killed 36 people and injured 140 others. According to the Ukrainian State Emergency Service, a total of 619 rescue workers and 132 equipment participated in the rescue work across Ukraine that day. Ukrainian President Zelensky said on social media on the 8th that Russia launched more than 40 missiles of various types at Ukraine that day. Residential buildings and infrastructure in many cities in Ukraine were damaged in varying degrees of attacks, and a children's hospital was destroyed. Rescue departments are currently conducting emergency rescue on the scene. The Russian Ministry of Defense issued a statement on the 8th local time saying that Ukrainian officials' claim that Russia used missiles to attack Ukrainian civilian facilities was untrue. The damage suffered by Kiev was caused by the fall of missiles launched by the city's air defense system.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.
Iran's president-elect reaffirms policy toward Israel
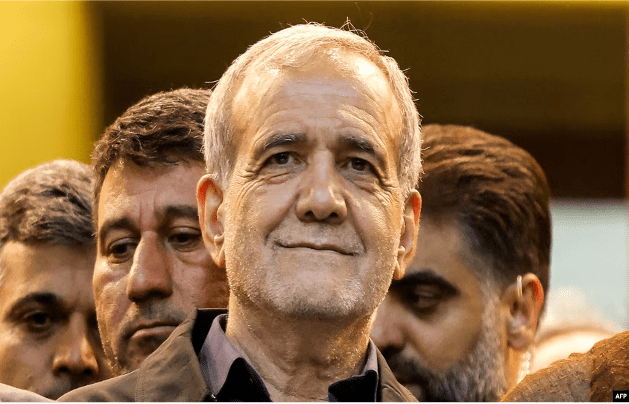
Iran's President-elect Masoud Pezeshkian reiterated Iran's anti-Israel stance on Monday, saying resistance movements across the region will not allow Israel's "criminal policies" against Palestinians to continue. Pezeshkian told Hassan Nasrallah, the leader of Iran-backed Lebanese Hezbollah, that "the Islamic Republic will always support the people of the region in their resistance against the illegal Zionist regime." This suggests that the incoming government will not change its regional policy under the relatively moderate Pezeshkian, who defeated his hard-line opponent in a runoff election last week. Pezeshkian was quoted as saying by Iranian media, "I am sure that the regional resistance movement will not allow this regime to continue its militant and criminal policies against the oppressed people of Palestine and other countries in the region." The Shiite Muslim Hezbollah and the Palestinian Sunni Muslim Hamas are both part of the local "resistance axis" faction organization supported by Iran. Israel did not immediately comment on Pezeshkian's speech. Hamas led an attack on southern Israel on October 7. According to Israeli statistics, Hamas killed 1,200 people and kidnapped about 250 hostages, triggering the Israeli-Palestinian war. The Gaza Health Ministry said that the Israeli military attack killed more than 38,000 Palestinians and injured nearly 88,000 people.