link1s.site

Portadown businessman avoids jail for sexual assault of teen under his employment Defence said the defendant 'continues to deny' the charges and bail in the sum of £1,000 was fixed for appeal

A Portadown man has avoided jail after sexually assaulting a 16-year-old shop worker under his employment.

-ADVERTISEMENT-

Brian Thomas Chapman (58), of Moyallan Road, appeared before Newry Magistrates’ Court on Monday for sentencing on two counts of sexual assault.

The prosecution outlined that on September 23, 2020, a 16-year-old student in the employment of Brian Chapman, disclosed to her mother about incidents that had occurred in her workplace.

She said Chapman had put his hand on her thigh and the back of her leg. She also disclosed that she had been getting extra money from him and he had been sending her text messages.

The allegations were reported to police the next day, September 24.

The victim then took part in an interview on October 9, in which she said, when she was alone in Chapman’s office, he placed his hand on her upper thigh and his other hand on her lower back, underneath her trousers.

The defendant was arrested and interviewed at Lurgan police station, where he denied the allegations. His phone was seized and an examination was carried out.

The first interview of the defendant took place on October 9, during which he admitted to sending a message about wanting the victim to work 24/7, but stated this was a joke.

The second interview took place on January 28, 2021, where he admitted to sending the 24/7 message, but denied sending other messages, such as “hope you’re spending the pounds on something special”.

Throughout this process, Chapman denied sending the messages and denied any of the sexual assaults alleged by the victim.

On the Chapman’s criminal record, the prosecution added that he was convicted of three common assaults on appeal.

In terms of commission, these matters pre-dated this case but the conviction occurred during the running of this case and also involved a female working for the defendant.

Prosecution continued that the age of the victim was an aggravating feature, arguing there was a “vulnerability” due to the “power-imbalance” between Chapman and the young student working for him.

An additional aggravating feature, they said, was that during the course of the defence, part of the defence was that the victim had “manipulated or manufactured” some of the text messages that were sent.

A defence lawyer, speaking on the pre-sentence report, noted the author deemed Chapman to be of low risk. He also noted that similar offences were contested in the County Court in respect of another complaint, with the judge substituting indecent assault charges for common assault.

He also argued a Sexual Offences Prevention Order (SOPO) was not necessary as the offending was four years ago, there has been no repetition and risk had been addressed.

District Judge Eamonn King noted the defendant was convicted on two of four original charges following a contest, which ran over a number of days, with the case adjourned for a pre-sentence report and victim impact statement to be produced.

He added the defendant “continues to deny” the charges and seeks to appeal the outcome.

District Judge King, on reading the pre-sentence report, noted the defendant “denies ever hugging or touching the individual and he denies any sexual attraction to the victim”, but pointed to a paragraph in the report which stated, “From the available evidence, it’s possible to surmise that he demonstrated risk taking and impulsive behaviour. It appears that he took advantage of his position and power in a bid to meet his sexual needs, given the victim’s young age and the fact that he was her employer”.

The report added that this demonstrated “limited victim empathy and responsibility due to his denial of the offences”.

On the victim impact statement, District Judge King described her as a young girl getting her first job, with the “world as her oyster”.

He continued: “As a result of what she says occurred, that turned on its head. It left her feeling inwardly uncomfortable, anxious and lonely. She cut herself off from her friends. She stopped going out. She didn’t want to go to school.”

He also described a “degree of manipulation” in the case, as this was the victim’s first job and there was a power imbalance between her as an employee, and Chapman as the employer.

In his sentencing remarks, District Judge King, said: “I’ve taken time to emphasise to the victim in this case that the victim did nothing wrong. The victim did everything right and the victim shouldn’t feel lonely, anxious or isolated.

“The victim should feel confident, strong and outgoing.”

Owing to the defendant’s ongoing denial of the charges, he added: “My sentencing exercise isn’t the conclusion of the case today, but I will sentence, so that we can move towards the conclusion going forward.

“I am satisfied, irrespective of what the pre-sentence report says, that the defendant took advantage of someone, attempted to groom someone and was guilty of the two offences.”

On the two counts, Chapman was sentenced to three months in prison, suspended for two years. He was also made subject to a Sexual Offences Prevention Order (SOPO) for five years and placed on the sex offenders’ register for seven years.

Following sentencing, District Judge King fixed bail for appeal at £1,000.
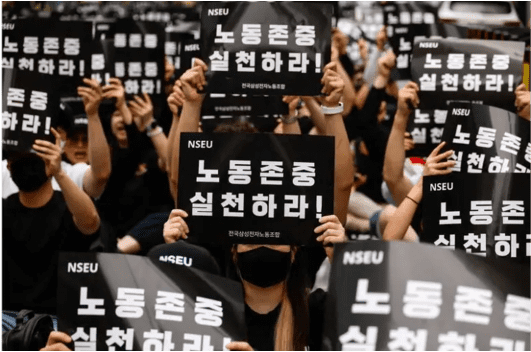
Samsung hit the biggest strike! Over 6,500 people attended.
More than 6,500 employees at South Korea's Samsung Electronics began a three-day mass strike on Monday (July 8), demanding an extra day of paid annual leave, higher pay raises and changes to the way performance bonuses are currently calculated. This is the largest organized strike in Samsung Electronics' more than half century of existence, and the union said that if this strike does not push employees' demands to be met, a new strike may be called. One of the core issues of the current dispute between the labor union and Samsung Electronics is raising wages and increasing the number of paid vacation days. The second demand is a pay rise. The union originally wanted a pay rise of more than 3% for its 855 employees, but last week they changed their demand to include all employees (rather than just 855). The third issue involves performance bonuses linked to Samsung's outsized profits - chip workers did not receive the bonuses last year when Samsung lost about Won15tn and, according to unions, fear they will still not get the money even if the company manages to turn around this year.
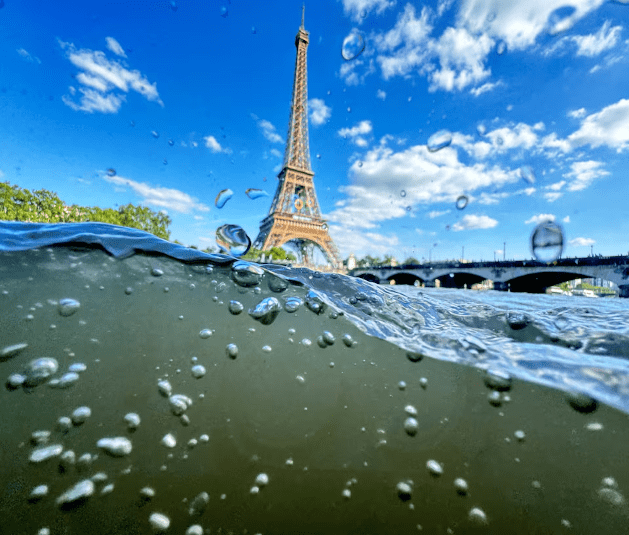
Insurers fret over militant attacks, AI hacks at Paris Olympics
LONDON, July 5 (Reuters) - Insurers are nervous that militant attacks or AI-generated fake images could derail the Paris Olympics, risking event cancellations and millions of dollars in claims. Insurers faced losses after the 2020 Tokyo Olympics were postponed for a year due to the COVID-19 pandemic. Since then, wars in Ukraine and Gaza and a spate of elections this year, including in France, have driven up fears of politically-motivated violence at high-profile global events. The Olympics take place in Paris from July 26-Aug 11 and the Paralympics from Aug 28-Sept 8. German insurer Allianz (ALVG.DE), opens new tab is insurance partner for the Games. Other insurers, such as the Lloyd's of London (SOLYD.UL) market, are also providing cover. "We are all aware of the geopolitical situation the world is in," said Eike Buergel, head of Allianz's Olympic and Paralympic programme. "We are convinced that the IOC (International Olympic Committee), Paris 2024 and the national organising committees, together with the French authorities, are taking the right measures when it comes to challenges on the ground."
Will chatGPT lead to job losses?
In fact, ChatGPT can bring more opportunities to many industries, such as customer service, marketing, speech recognition, and more. ChatGPT can help businesses engage with customers more effectively, improve the customer experience, and give businesses more time and resources to focus on other tasks. Come to see While ChatGPT can replace humans in certain situations, it is not a complete replacement for humans. In many cases, human-to-human communication is still the most effective way. Therefore, the emergence of ChatGPT will not lead to the unemployment of all people, but will cause structural changes in the labor force and the redistribution of occupations.
Xinjiang scientists discover plant with potential to survive on Mars
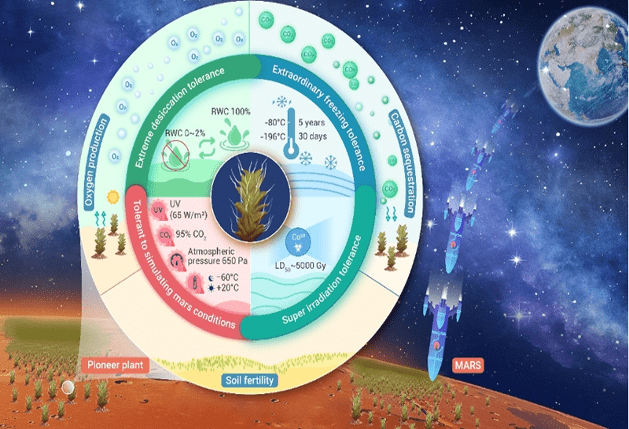
In a groundbreaking discovery, researchers from the Xinjiang Institute of Ecology and Geography of the Chinese Academy of Sciences have found a desert moss species, known as Syntrichia caninervis, that has the potential to survive in the extreme conditions on Mars. The Global Times learned from the institute that during the third Xinjiang scientific expedition, the research team focused on studying the desert moss and found that it not only challenges people's understanding of the tolerance of organisms in extreme environments, but also demonstrates the ability to survive and regenerate under simulated Martian conditions. Supported by the Xinjiang scientific expedition project, researchers Li Xiaoshuang, Zhang Daoyuan and Zhang Yuanming from the Xinjiang Institute of Ecology and Geography and Kuang Tingyun, an academician from the Chinese Academy of Sciences, concentrated on studying the "pioneer species" Syntrichia caninervis in an extreme desert environment, according to the institute in an article it sent to the Global Times on Sunday. Through scientific experiments, the researchers systematically proved that the moss can tolerate over 98 percent cell dehydration, survive at temperatures as low as -196 C without dying, withstand over 5000Gy of gamma radiation without perishing, and quickly recover, turn green, and resume growth, showcasing extraordinary resilience. These findings push the boundaries of human knowledge on the tolerance of organisms in extreme environments. Furthermore, the research revealed that under simulated Martian conditions with multiple adversities, Syntrichia caninervis can still survive and regenerate when returned to suitable conditions. This marks the first report of higher plants surviving under simulated Martian conditions. The research team also identified unique characteristics of Syntrichia caninervis. Its overlapping leaves reduce water evaporation, while the white tips of the leaves reflect intense sunlight. Additionally, the innovative "top-down" water absorption mode of the white tips efficiently collects and transports water from the atmosphere. Moreover, the moss can enter a selective metabolic dormancy state in adverse environments and rapidly provide the energy needed for recovery when its surrounding environment improves. Based on the extreme environmental tolerance of Syntrichia caninervis, the research team plans to conduct experiments on spacecraft to monitor the survival response and adaptation capabilities of the species under microgravity and various ionizing radiation adversities. They aim to unravel the physiological and molecular basis of the moss and explore the key life tolerance regulatory mechanisms, laying the foundation for future applications of Syntrichia caninervis in outer space colonization.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.