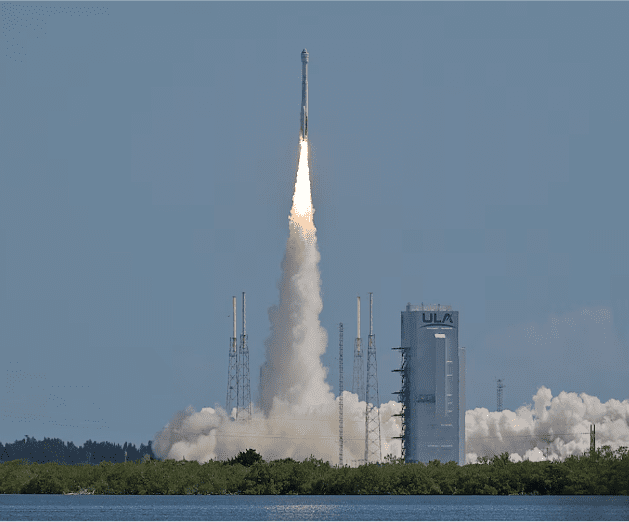
Explainer: How Boeing's Starliner can bring its astronauts back to Earth
WASHINGTON, June 24 (Reuters) - Problems with Boeing's Starliner capsule, still docked at the International Space Station (ISS), have upended the original plans for its return of its two astronauts to Earth, as last-minute fixes and tests draw out a mission crucial to the future of Boeing's (BA.N), opens new tab space division. NASA has rescheduled the planned return three times, and now has no date set for it. Since its June 5 liftoff, the capsule has had five helium leaks, five maneuvering thrusters go dead and a propellant valve fail to close completely, prompting the crew in space and mission managers in Houston to spend more time than expected pursuing fixes mid-mission. Here is an explanation of potential paths forward for Starliner and its veteran NASA astronauts, Barry "Butch" Wilmore and Sunita "Suni" Williams. THE CURRENT SITUATION Starliner can stay docked at the ISS for up to 45 days, according to comments by NASA's commercial crew manager Steve Stich to reporters. But if absolutely necessary, such as if more problems arise that mission officials cannot fix in time, it could stay docked for up to 72 days, relying on various backup systems, according to a person familiar with flight planning. Internally at NASA, Starliner's latest targeted return date is July 6, according to this source, who spoke on condition of anonymity. Such a return date would mean that the mission, originally planned for eight days, instead would last a month. Starliner's expendable propulsion system is part of the craft's "service module." The current problems center on this system, which is needed to back the capsule away from the ISS and position it to dive through Earth's atmosphere. Many of Starliner's thrusters have overheated when fired, and the leaks of helium - used to pressurize the thrusters - appear to be connected to how frequently they are used, according to Stich.
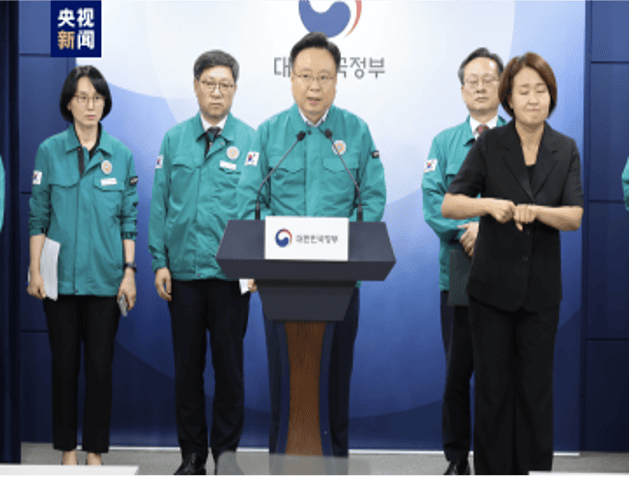
South Korean government decides not to punish interns who resign
South Korea's Minister of Health and Welfare Cho Kyu-hong said at a press conference on the 8th local time that after comprehensively considering the suggestions of frontline interns and the situation on the front line of medical care, the government decided that from that day on, all interns and residents who resigned would not be given administrative sanctions such as revoking their medical licenses. Cho Kyu-hong also said that for interns and residents who have returned to work and those who have resigned and are preparing to re-register for internship courses in September, the government will make special cases to try to minimize the internship gap and not affect the relevant doctors from obtaining specialist medical licenses. Cho Kyu-hong said that the government believes that in order to minimize the diagnosis and treatment gaps for critically ill and emergency patients and ensure the smooth training process of interns and residents, it is in the public interest, so it has made a decision not to punish interns and residents who resigned. It is hoped that major hospitals will complete the resignation processing of doctors who have not returned to work before July 15 and determine the scale of vacancies. Previously, large general hospitals in South Korea, such as Seoul National University Hospital, Yonsei University Severance Hospital, and Seoul Asan Medical Center, suspended or limited their medical services in an effort to cancel all penalties against interns and residents.
Google extends Linux kernel support to 4 years
According to AndroidAuthority, the Linux kernel used by Android devices is mostly derived from Google's Android Universal Kernel (ACK) branch, which is created from the Android mainline kernel branch when new LTS versions are released upstream. For example, when kernel version 6.6 is announced as the latest LTS release, an ACK branch for Android15-6.6 appears shortly after, with the "android15" in the name referring to the Android version of the kernel (in this case, Android 15). Google maintains its own set of LTS kernel branches for three main reasons. First, Google can integrate upstream features that have not yet been released into the ACK branch by backporting or picking, so as to meet the specific needs of Android. Second, Google can include some features that are being developed upstream in the ACK branch ahead of time, making it available for Android devices as early as possible. Finally, Google can add some vendor or original equipment manufacturer (OEM) features for other Android partners to use. Once created, Google continues to update the ACK branch to include not only bug fixes for Android specific code, but also to integrate the LTS merge content of the upstream kernel branch. For example, the Linux kernel vulnerability disclosed in the July 2024 Android security bulletin will be fixed through these updates. However, it is not easy to distinguish a bug fix from other bug fixes, as a patch that fixes a bug may also accidentally plug a security vulnerability that the submitter did not know about or chose not to disclose. Google does its best to recognize this, but it inevitably misses the mark, resulting in bug fixes for the upstream Linux kernel being released months before Android devices. As a result, Google has been urging Android vendors to regularly update the LTS kernel to avoid being caught off guard by unexpectedly disclosed security vulnerabilities. Clearly, the LTS version of the Linux kernel is critical to the security of Android devices, helping Google and vendors deal with known and unknown security vulnerabilities. The longer the support period, the more timely security updates Google and vendors can provide to devices.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.
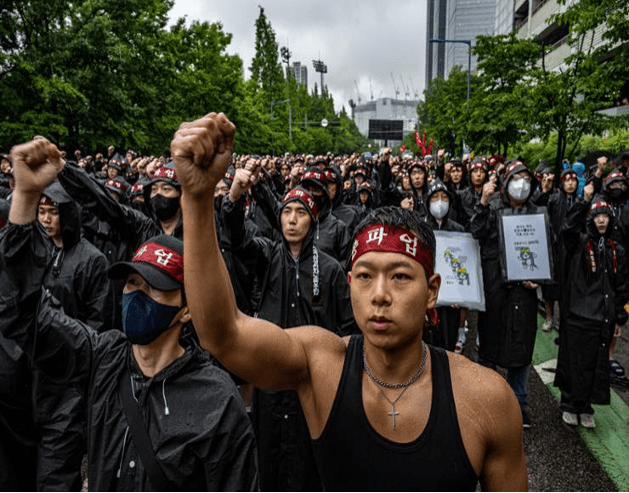
Workers warn of additional walkouts unless demands are met
Members of the National Samsung Electronics Union stage a rally near the company's Hwaseong Campus in Gyeonggi Province, Monday, beginning a three-day strike. Korea Times photo by Shim Hyun-chul By Nam Hyun-woo The biggest labor union at Samsung Electronics initiated a three-day strike on Monday, threatening to disrupt the company's chip manufacturing lines unless management agrees to a wage hike and higher incentives. This marks the first strike by unionized workers in the tech giant's 55-year history. The National Samsung Electronics Union (NSEU) claimed that about 4,000 unionized workers from Samsung's plants nationwide participated in a rally at the company's Hwaseong Campus in Gyeonggi Province. Police estimated that approximately 3,000 union members were present at the rally. According to its own survey, the union reported that a total of 6,540 members expressed their intention to participate in the strike. They emphasized that disruptions in manufacturing are anticipated, with over 5,000 members from facility, manufacturing, and development divisions joining the strike. The comments seem to address market expectations that the walkout is unlikely to cause significant disruptions in the chipmaker's operations, largely because most manufacturing lines are automated. The union said that it may launch another strike for an undetermined period, unless management responds to the union’s demand. Since January, the union has been pressing management for a higher wage increase rate for all members, fulfillment of promises regarding paid leave, and improvements to incentive criteria. With negotiations at an impasse, the union announced on May 29 that it would launch a strike. The NSEU has some 30,000 members, accounting for 24 percent of all Samsung employees. Among the union members, about 80 percent work at the device solutions division, which manufactures semiconductors.