WhatsApp's new feature will let Meta AI edit your photos for you
WhatsApp beta version 2.24.14.20 has a new feature that allows users to share photos with Meta AI. The AI chatbot will analyze uploaded images and provide information or context about the content. Users may be able to request specific edits to their photos directly through Meta AI, though the extent of this feature is still unknown. As the battle for AI dominance heats up, Meta is adding a new trick to its AI chatbot, Meta AI, which is already part of Facebook, Instagram, and WhatsApp. While Meta AI already has impressive text capabilities, such as replying to questions, suggesting captions, and holding conversations, users cannot currently share or upload photos to the Meta AI chat. WaBetaInfo has uncovered the exciting new feature in the WhatsApp beta for Android version 2.24.14.20. This feature will allow Meta AI to interact with photos shared by users, reply to photos, and even edit them. As shown in the attached screenshot, WhatsApp is testing a new camera button in the Meta AI chat, designed to function similarly to the camera button in regular chats. This addition will allow users to manually share photos with Meta AI, a capability that is currently unavailable. With this new functionality, users will be able to ask questions about their photos, presumably allowing users to ask the AI to identify objects or locations or provide context about the photo’s content. Moreover, the screenshot suggests that Meta AI will also offer the option to edit photos, enabling users to make changes to their images directly within the chat by sharing a prompt. The exact scope of this image editing feature remains unclear, leaving us to wonder if it will be limited to simple tweaks or if it will unleash a powerful AI-driven photo editing suite. The possibilities are both exciting and intriguing, and this feature could definitely be a big hit, especially if it performs as promised. While this new image-sharing feature would mean Meta will analyze and face-scan the photos you upload, the screenshot includes a disclaimer indicating that users will have the option to delete their photos whenever they want. As of now, it seems that the feature is still in development, so it might be some time before we finally get to see it roll out publicly. Recently, we also reported about WhatsApp working on an “Imagine Me” feature that would allow Meta AI to generate AI avatars of you based on a set of your photos. WhatsApp in our newsletters WhatsApp is a leading messaging app, keep up to date on the latest, and learn about more Android apps today!
Former British PM Sunak appoints Conservative Party shadow cabinet
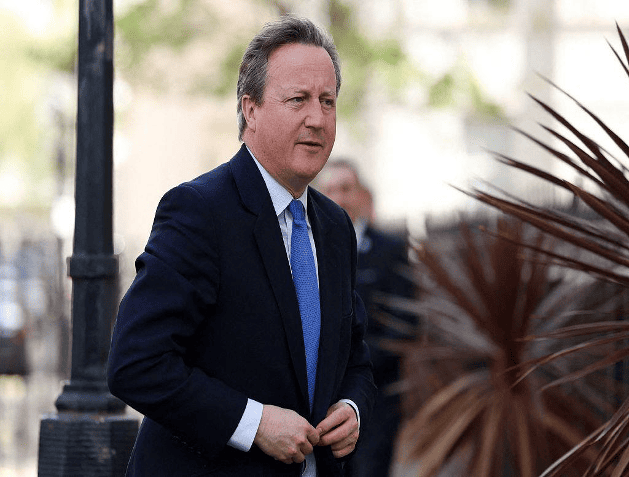
On July 8, local time, former British Prime Minister Sunak announced the appointment of the Conservative Party Shadow Cabinet, which is the first shadow cabinet of the Conservative Party in 14 years. Several former British cabinet members during Sunak's tenure as prime minister were appointed to the Conservative Party Shadow Cabinet, including James Cleverly as Shadow Home Secretary and Jeremy Hunt as Shadow Chancellor of the Exchequer. But former Foreign Secretary Cameron was not appointed as Shadow Foreign Secretary. In addition, the new leader of the Conservative Party will be elected as early as this week. On July 4, the UK held a parliamentary election. The counting results showed that the British Labour Party won more than half of the seats and won an overwhelming victory; the Conservative Party suffered a disastrous defeat, ending its 14-year continuous rule.
The largest password leak in history exposes nearly 10 billion credentials
The largest collection of stolen passwords ever has been leaked to a notorious crime marketplace, according to cybersecurity researchers at Cybernews. This leak, dubbed RockYou2024 by its original poster “ObamaCare,” holds a file containing nearly 10 billion unique plaintext passwords. Allegedly gathered from a series of data breaches and hacks accumulated over several years, the passwords were posted on July 4th and hailed as the most extensive collection of stolen and leaked credentials ever seen on the forum. “In its essence, the RockYou2024 leak is a compilation of real-world passwords used by individuals all over the world,” the researchers told Cybernews. “Revealing that many passwords for threat actors substantially heightens the risk of credential stuffing attacks.” Credential stuffing attacks are among the most common methods criminals, ransomware affiliates, and state-sponsored hackers use to access services and systems. Threat actors could exploit the RockYou2024 password collection to conduct brute-force attacks against any unprotected system and “gain unauthorized access to various online accounts used by individuals whose passwords are included in the dataset,” the research team said. This could affect online services, cameras and hardware This could affect various targets, from online services to internet-facing cameras and industrial hardware. “Moreover, combined with other leaked databases on hacker forums and marketplaces, which, for example, contain user email addresses and other credentials, RockYou2024 can contribute to a cascade of data breaches, financial frauds, and identity thefts,” the team concluded. However, despite the seriousness of the data leak, it is important to note that RockYou2024 is primarily a compilation of previous password leaks, estimated to contain entries from a total of 4,000 massive databases of stolen credentials, covering at least two decades. This new file notably includes an earlier credentials database known as RockYou2021, which featured 8.4 billion passwords. RockYou2024 added approximately 1.5 billion passwords to the collection, spanning from 2021 through 2024, which, though a massive figure, is only a fraction of the reported 9,948,575,739 passwords in the leak. Thus, users who have changed their passwords since 2021 may not have to panic about a potential breach of their information. That said, the research team at Cybernews stressed the importance of maintaining data security. In response to the leak, they recommend immediately changing the passwords for any accounts associated with the leaked credentials, ensuring each password is strong and unique and not reused across different platforms. Additionally, they advised enabling multi-factor authentication (MFA), which requires an extra form of verification beyond the password, wherever possible, to strengthen cyber security. Lastly, tech users should utilize password manager software, which securely generates and stores complex passwords, mitigating the risk of password reuse across multiple accounts.
Google extends Linux kernel support to 4 years
According to AndroidAuthority, the Linux kernel used by Android devices is mostly derived from Google's Android Universal Kernel (ACK) branch, which is created from the Android mainline kernel branch when new LTS versions are released upstream. For example, when kernel version 6.6 is announced as the latest LTS release, an ACK branch for Android15-6.6 appears shortly after, with the "android15" in the name referring to the Android version of the kernel (in this case, Android 15). Google maintains its own set of LTS kernel branches for three main reasons. First, Google can integrate upstream features that have not yet been released into the ACK branch by backporting or picking, so as to meet the specific needs of Android. Second, Google can include some features that are being developed upstream in the ACK branch ahead of time, making it available for Android devices as early as possible. Finally, Google can add some vendor or original equipment manufacturer (OEM) features for other Android partners to use. Once created, Google continues to update the ACK branch to include not only bug fixes for Android specific code, but also to integrate the LTS merge content of the upstream kernel branch. For example, the Linux kernel vulnerability disclosed in the July 2024 Android security bulletin will be fixed through these updates. However, it is not easy to distinguish a bug fix from other bug fixes, as a patch that fixes a bug may also accidentally plug a security vulnerability that the submitter did not know about or chose not to disclose. Google does its best to recognize this, but it inevitably misses the mark, resulting in bug fixes for the upstream Linux kernel being released months before Android devices. As a result, Google has been urging Android vendors to regularly update the LTS kernel to avoid being caught off guard by unexpectedly disclosed security vulnerabilities. Clearly, the LTS version of the Linux kernel is critical to the security of Android devices, helping Google and vendors deal with known and unknown security vulnerabilities. The longer the support period, the more timely security updates Google and vendors can provide to devices.
Doctors visited the White House 8 times? White House: Biden did not receive treatment for Parkinson's disease
White House spokeswoman Karina Jean-Pierre denied a report in the U.S. media on the 8th that President Joseph Biden did not receive treatment for Parkinson's disease. Biden had the first televised debate of the 2024 presidential election with Republican opponent Donald Trump on June 27, and his poor performance on the spot triggered discussions about his physical condition. The New York Times reported that a doctor specializing in the treatment of Parkinson's disease had "visited" the White House eight times from August last year to March this year. Facing the media's questions about Biden's health, Jean-Pierre asked and answered himself at a regular White House press conference on the 8th: "Has the president received treatment for Parkinson's disease? No. Is he currently receiving treatment for Parkinson's disease? No, he is not. Is he taking medication for Parkinson's disease? No." Jean-Pierre said Biden had seen a neurologist three times, all related to his annual physical examination. She also took out the report issued by the doctor after Biden's most recent physical examination in February this year. The report said, "An extremely detailed neurological examination was once again reassuring" because no symptoms consistent with stroke, multiple sclerosis or Parkinson's disease were found. The doctor who went to the White House mentioned by the New York Times is Kevin Kanal, a neurology and movement disorder expert at the Walter Reed National Military Medical Center in Maryland and an authority on Parkinson's disease. Jean-Pierre suggested that the doctor might have come to treat military personnel on duty at the White House.